Generic network firewall
Filters by IP, port, and protocol. Useful for segmentation, but blind to a crafted HTTP body aimed at your login form.
Secured by OVHcloud WAF
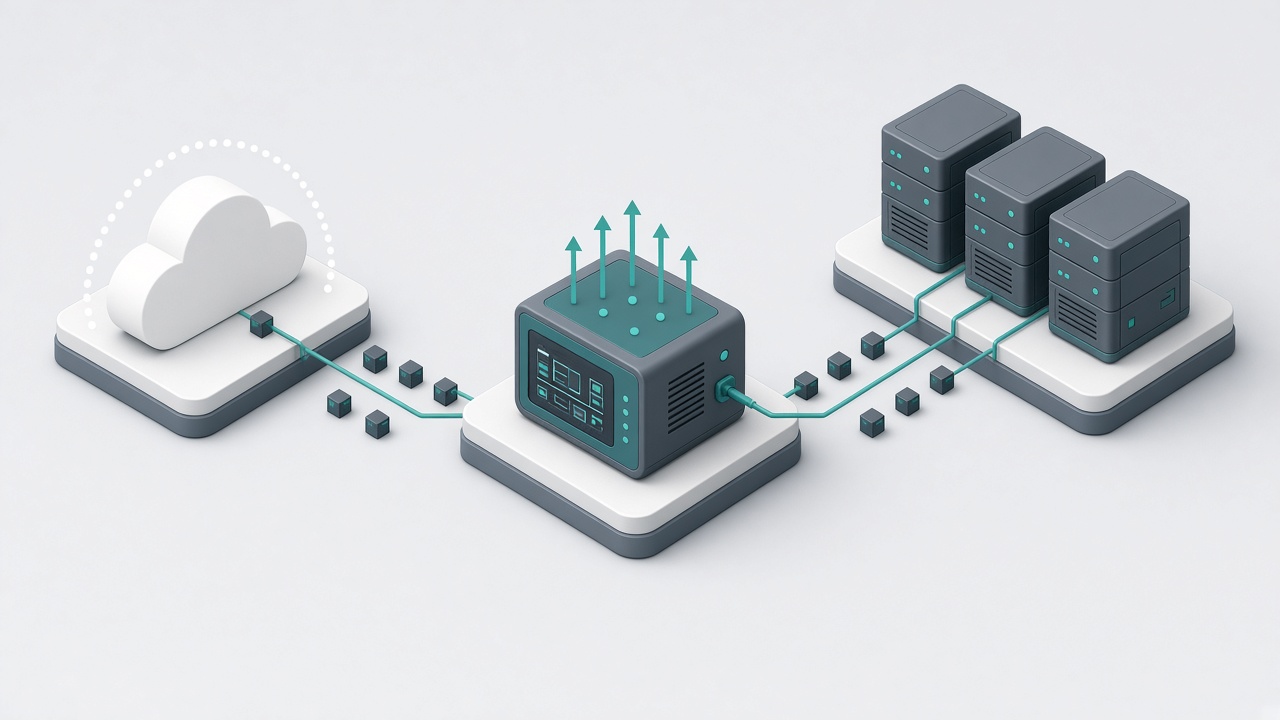
OWAF is OVHcloud’s Web Application Firewall. It protects internet-facing
applications and APIs against common attacks, with policies you control and data that stays
on OVHcloud infrastructure.
This demo origin (waf.success.ovh) is published behind it.
Filters by IP, port, and protocol. Useful for segmentation, but blind to a crafted HTTP body aimed at your login form.
Inspects HTTP/HTTPS at layer 7 with OWASP CRS 4.x: headers, body, URI, cookies, and query parameters — then blocks or proxies.
As described on the OVHcloud labs page.
| Topic | OWAF alpha |
|---|---|
| Placement | Inline between clients and your backend |
| Decision | 403 Forbidden, or proxy to origin over HTTP/HTTPS |
| Rules | OWASP Core Rule Set 4.x + optional custom rules |
| Configuration | Entirely via the WAF Console |
| Region | Europe — Gravelines (eu-west-gra) |
| TLS | Terminated by OVHcloud; certificate managed for you |
Enable or disable built-in CRS rules, override actions or paranoia level, and add custom rules (up to 500 per instance).
Requests, logs, and rules remain on OVHcloud — European sovereignty by design.
Switch between Blocking, Detection (log only), and Disabled without redeploying this origin.
Useful background if you are evaluating OWAF alongside this protected site.
Complete the form on the labs page. Access is at OVHcloud’s discretion.
Get your WAF and account access token.
Make your service domain point to the WAF ingress IP — the same pattern used for this host.
Configure policies at labs.waf.ovh.net.